Intezer
AI-driven cybersecurity automation, reducing SOC workload effectively.
Key Takeaways
- What it is
- AI-driven cybersecurity automation, reducing SOC workload effectively.
- Best for
- Autonomous Alert Triage
- AI-Powered Investigations
- Seamless Integration
- Rating
- 4.5/5
What is Intezer?
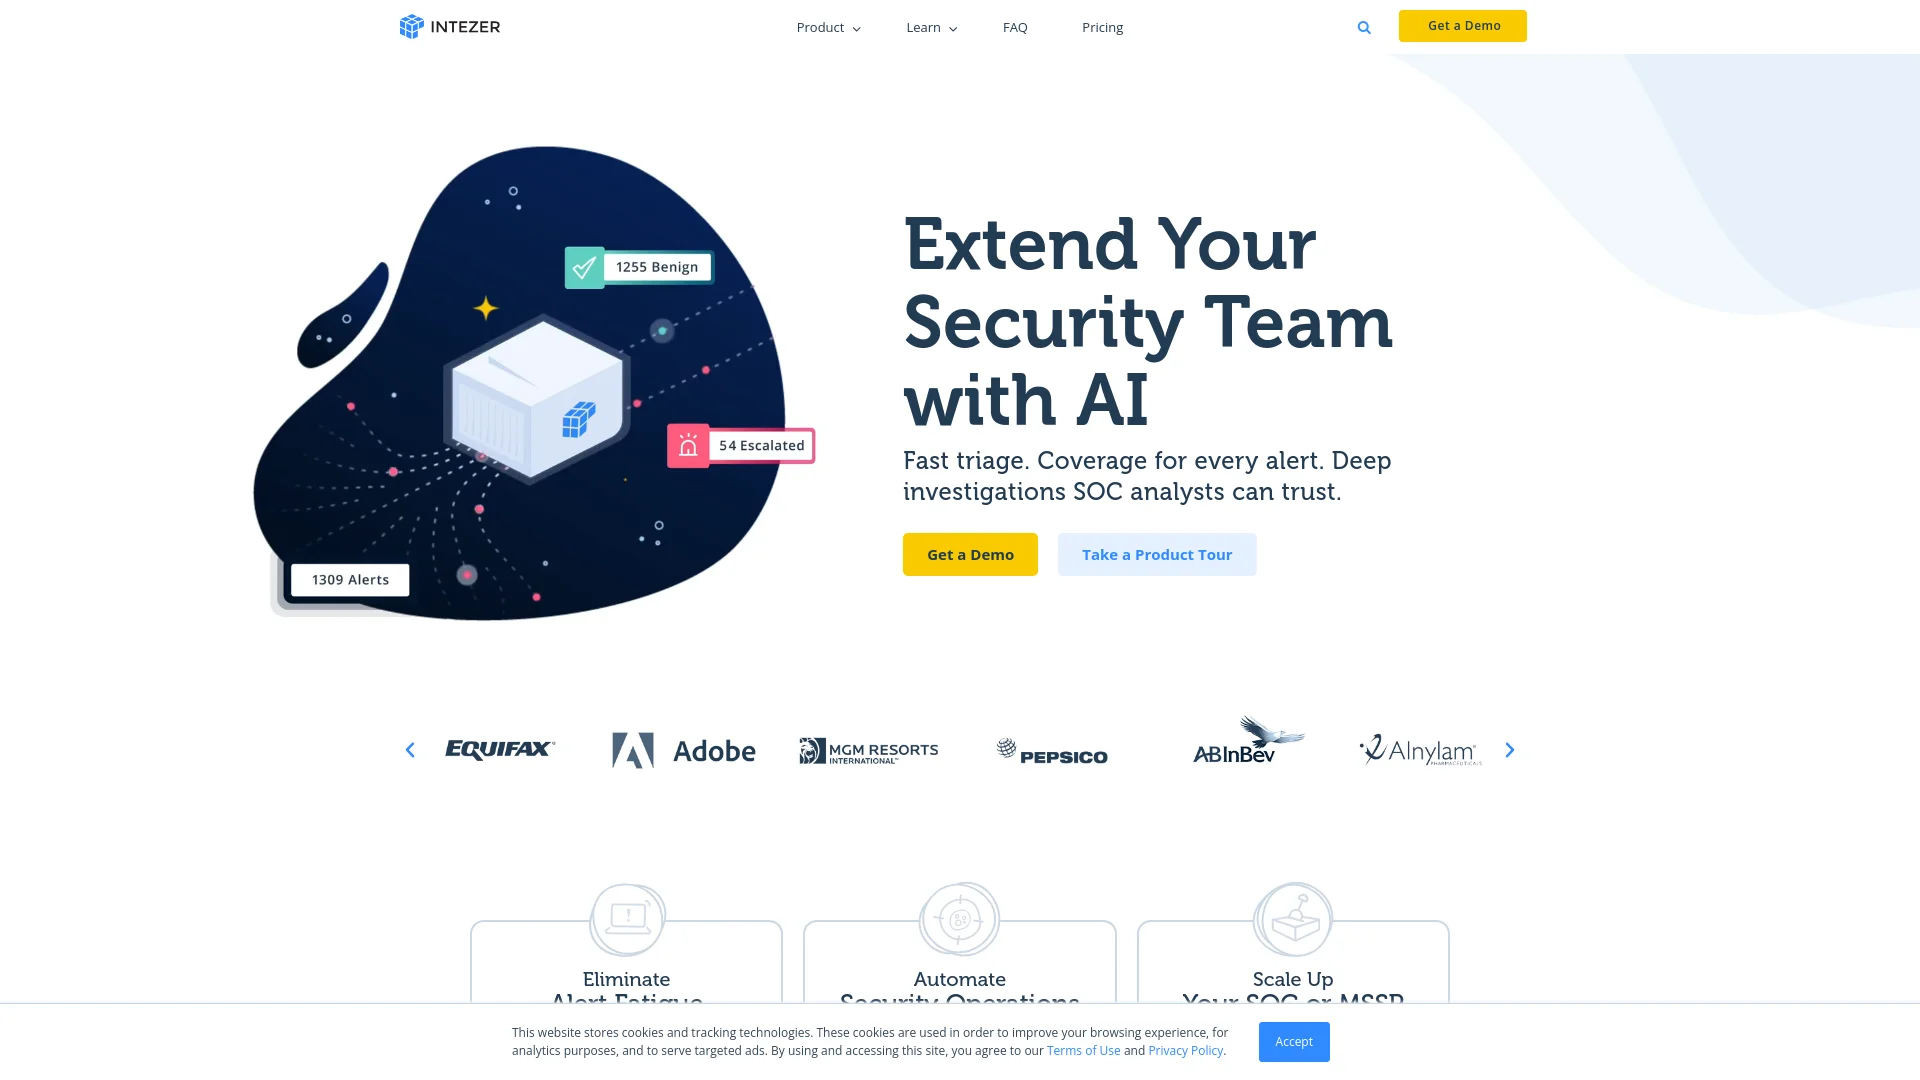
Intezer is a state-of-the-art cybersecurity solution designed to optimize the efficiency and effectiveness of Security Operations Centers (SOCs). The platform's Autonomous SOC capabilities leverage AI to automate the triage, investigation, remediation, and escalation of security threats, aiming to reduce the workload on security teams and improve response times. Intezer is particularly valuable for organizations looking to scale their security operations without increasing costs.
Intezer distinguishes itself by offering a truly autonomous SOC experience that extends beyond traditional automation tools such as SOAR playbooks and sandboxing. Its advanced AI engine not only automates responses but also provides intelligent decision-making support, setting a new benchmark for security operations efficiency.
Intezer excels in automating and streamlining SOC operations, providing significant reductions in manual workload and enhancing overall threat detection and response capabilities. Its AI-driven platform offers substantial time and cost savings while improving organizational security posture, making it an essential tool for modern SOCs and MSSPs.
Who is Using Intezer?
Large Enterprises
Managing high volumes of security alerts with enhanced efficiency.
Managed Security Service Providers (MSSPs)
Leveraging Intezer to provide advanced services to their clients through Autonomous SOC capabilities.
Healthcare Institutions
Securing sensitive patient data with sophisticated, AI-driven threat detection and triage.
Financial Institutions
Ensuring compliance and security of financial data with automated threat response and management.
Uncommon Use Cases
Used in academic settings for educational purposes in cybersecurity courses and by non-profits to secure donor data with limited IT resources.
Key Features
Rating Breakdown
Pricing Plans
Subscription Model
- Custom pricing tailored to the scale of operations and specific organizational needs
Free Demo
- Available for prospective users to explore features and capabilities with a product tour
Which Intezer plan should you pick?
Start with Starter when you need one alert source; upgrade to Complete when you need all alert sources, custom workflows, and broader response coverage.
Starter
Good for organizations that need 24/7 monitoring, automated triage, investigation, and response for one endpoint or phishing alert source.
Complete
Good for organizations that need unlimited alert sources, custom response workflows, case management options, and broader enterprise coverage.
Intezer Use Cases
Reported phishing triage
Intezer vets reported emails, links, and attachments and returns verdicts with priority, classification, and context.
Outcome: Faster verdicts and fewer unnecessary escalations.
Endpoint alert triage
Intezer collects and analyzes files, processes, logs, command lines, and memory images from endpoint alerts.
Outcome: False positives are resolved while real threats are escalated.
SIEM alert triage
Intezer investigates SIEM alerts and surfaces the threats that matter from high-volume alert streams.
Outcome: Security teams receive prioritized investigations.
Identity alert triage
Intezer investigates suspicious logins, account activity, and anomalies from identity providers.
Outcome: Identity-alert noise and response time are reduced.
Cloud alert triage
Intezer investigates risky administrative access and runtime activity across cloud environments.
Outcome: Cloud threats are surfaced and false positives can be automatically resolved.
Workflow Ideas with Intezer
Close false positives and notify analysts
- 1Trigger the workflow from a forensic verdict
- 2Close the false positive in the connected SIEM
- 3Notify the responsible analyst in Slack
Automate endpoint containment
- 1Receive an escalated incident or case event
- 2Apply conditional routing based on the investigation
- 3Isolate the affected host and log the workflow run
Route investigation results to ticketing
- 1Trigger a workflow from an alert or webhook
- 2Update the connected ticket with the investigation context
- 3Escalate the incident for human review when conditions are met
How Intezer fits into your stack
Broad Integration Support
Works with major SIEM systems, endpoint protection platforms, and SOAR solutions.
API Access
Provides a robust API for custom integrations, allowing for tailored platform functionality.
Plugin Ecosystem
Supports a range of plugins for enhanced integration flexibility and functionality.
Pros
- +Increased Efficiency: Cuts down the time and effort spent on manual alert triage and analysis, allowing teams to focus on more critical tasks.
- +Cost Reduction: Automates repetitive tasks, reducing operational costs and resource needs.
- +Scalability: Facilitates scaling of SOC operations by efficiently handling larger volumes of alerts without requiring additional staff.
- +Enhanced Accuracy: Reduces human error and improves the accuracy of threat detection and response.
Cons
- −Complex Setup: Requires a detailed initial setup and fine-tuning to meet specific organizational needs, which can be complex.
- −Learning Curve: New users might need time to understand the platform's full capabilities and best practices.
- −Integration Dependency: The platform’s full efficacy is achieved when integrated with other security tools, which could be a challenge for organizations with incompatible existing systems.
Limitations & when to consider alternatives
Known limitations
- Starter supports one alert source. The Starter plan is limited to one alert source, either endpoint or user-reported phishing.
- Complete is required for all alert sources. SIEM, cloud, identity, and network sources are included under Complete rather than Starter.
- Managed SIEM is an add-on. Managed SIEM is not part of the standard base package and must be added separately.
- Workflows were initially early access. Intezer announced workflow availability first for selected customers, with general availability planned later.
- Pricing is endpoint-based. The published pricing model is based on endpoint count rather than a publicly displayed flat monthly price.
Look elsewhere when
- You need a native mobile application.
- You need visual image analysis.
- You need a coding assistant that generates or edits code.
How to Use Intezer
- 1
Comprehensive tutorials and documentation are available on the Intezer website, covering everything from initial setup to advanced operational techniques.
Who is Intezer For?
Enterprise security teams
The platform investigates and responds to high volumes of alerts across endpoint, SIEM, identity, cloud, network, and email sources.
Security operations centers
Intezer automates Tier 1 and Tier 2 alert triage so analysts can focus on escalated threats and strategic security work.
Managed security service providers
Endpoint-based pricing and multi-source alert investigation support MSSP growth and broad customer coverage.
Incident response teams
Forensic analysis, memory scanning, reverse engineering, sandboxing, and threat intelligence support investigation and remediation.
Frequently Asked Questions
How does Intezer's AI SOC work?
Intezer combines proprietary and commercial AI models with forensic tools to produce incident-triage assessments.
What security tools does Intezer integrate with?
Intezer offers bidirectional integrations with security detection tools, SIEMs, asset-management systems, ticketing platforms, and SOARs.
How is Intezer different from a SOAR or MDR?
Intezer automates alert-triage and investigation decision-making, while SOAR platforms focus on case management and repetitive playbooks.
What is the setup process and how long does it take?
Connect alert sources with API keys and add team members. Intezer says alert-triage results can begin appearing within an hour.
What kind of companies and security teams use Intezer?
Intezer says enterprise security teams, including organizations such as Equifax, MGM Resorts, and NVIDIA, use the platform.
How is Intezer priced?
Intezer uses endpoint-based pricing. Starter supports one alert source, while Complete supports all alert sources.
Community reviews
Be the first to share your experience.
Sign in to leave a review for Intezer.
Intezer Alternatives
Looking for alternatives to Intezer? Here are similar tools in the same category:
Learn to Master Intezer
With Skill Leap courses
Get in-depth training on Intezer and 50+ other AI tools with our expert-led video courses.
Start 7-Day Free Trial